


Gately
开源网络网关工具集,DDNS/STUN/端口转发/反代/证书/WAF 一体
安装次数
点赞
应用评论
催更次数
桌面端

应用描述
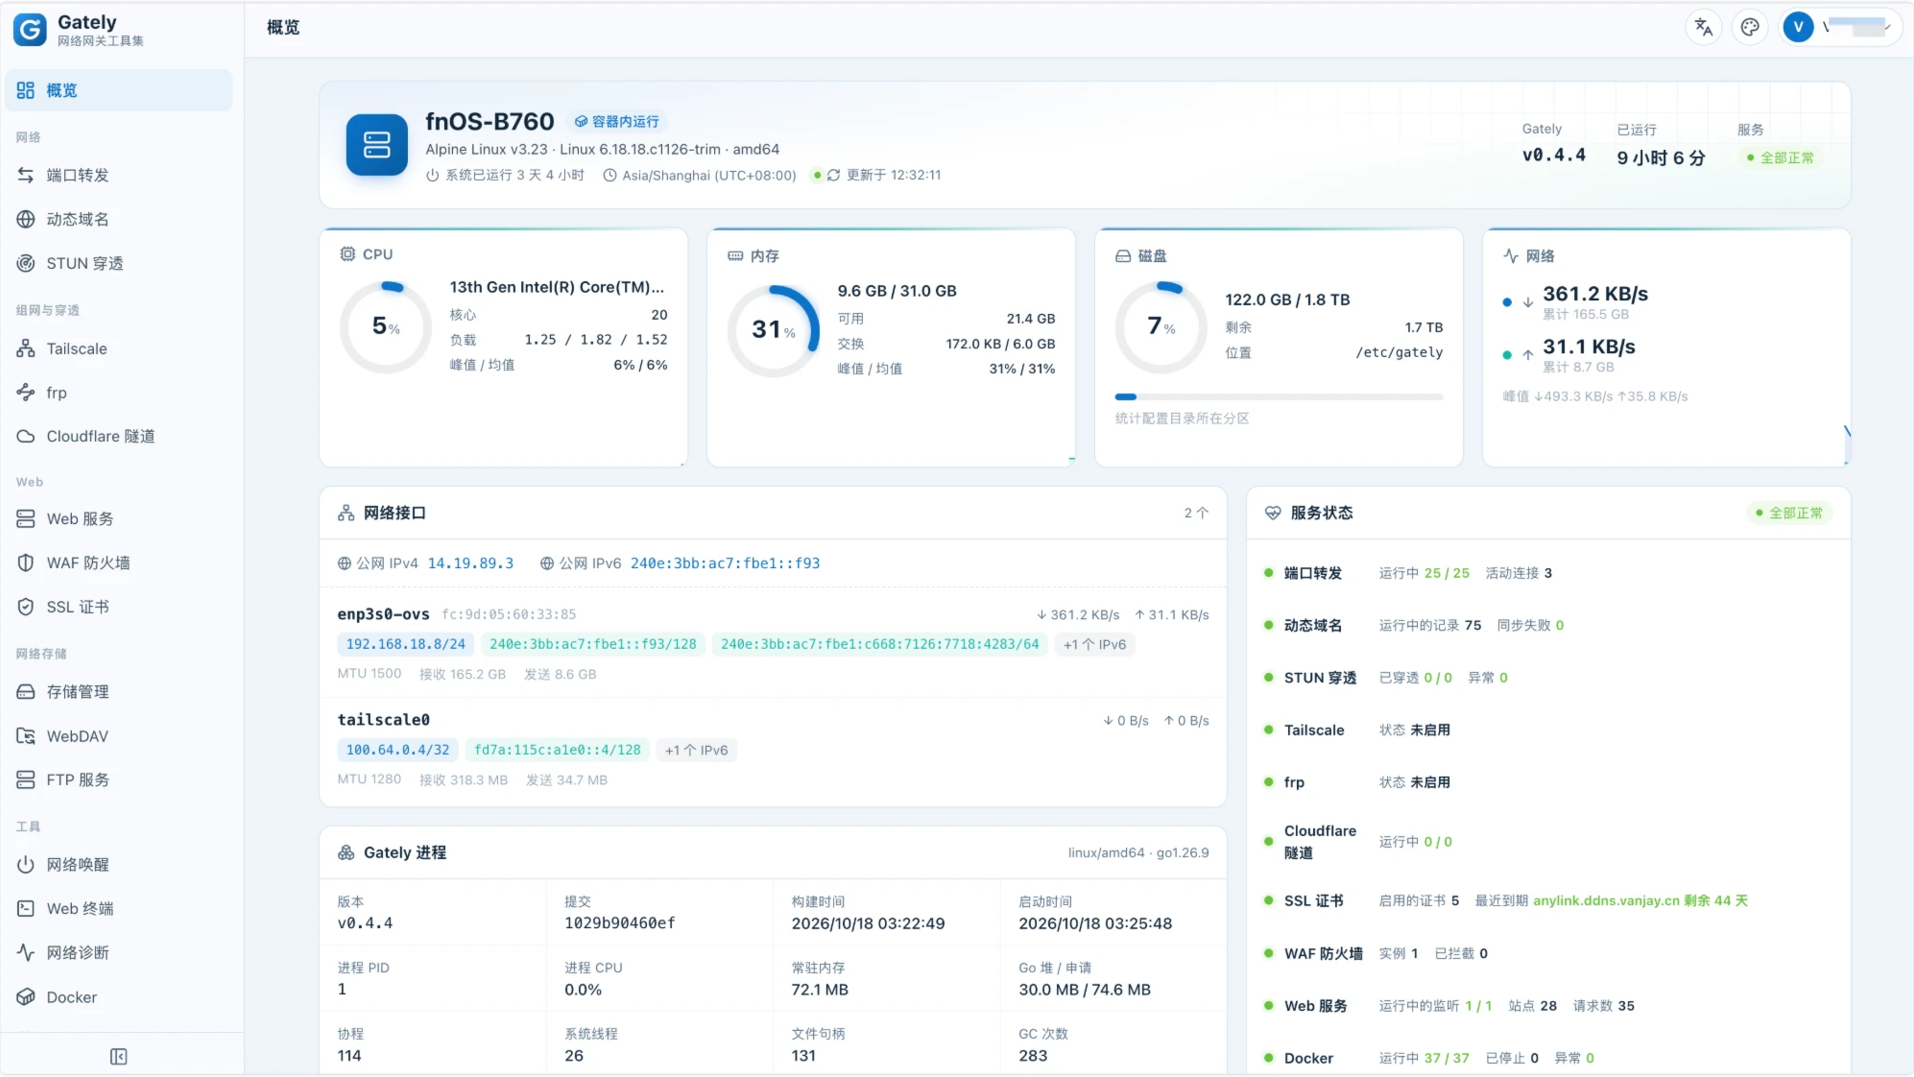
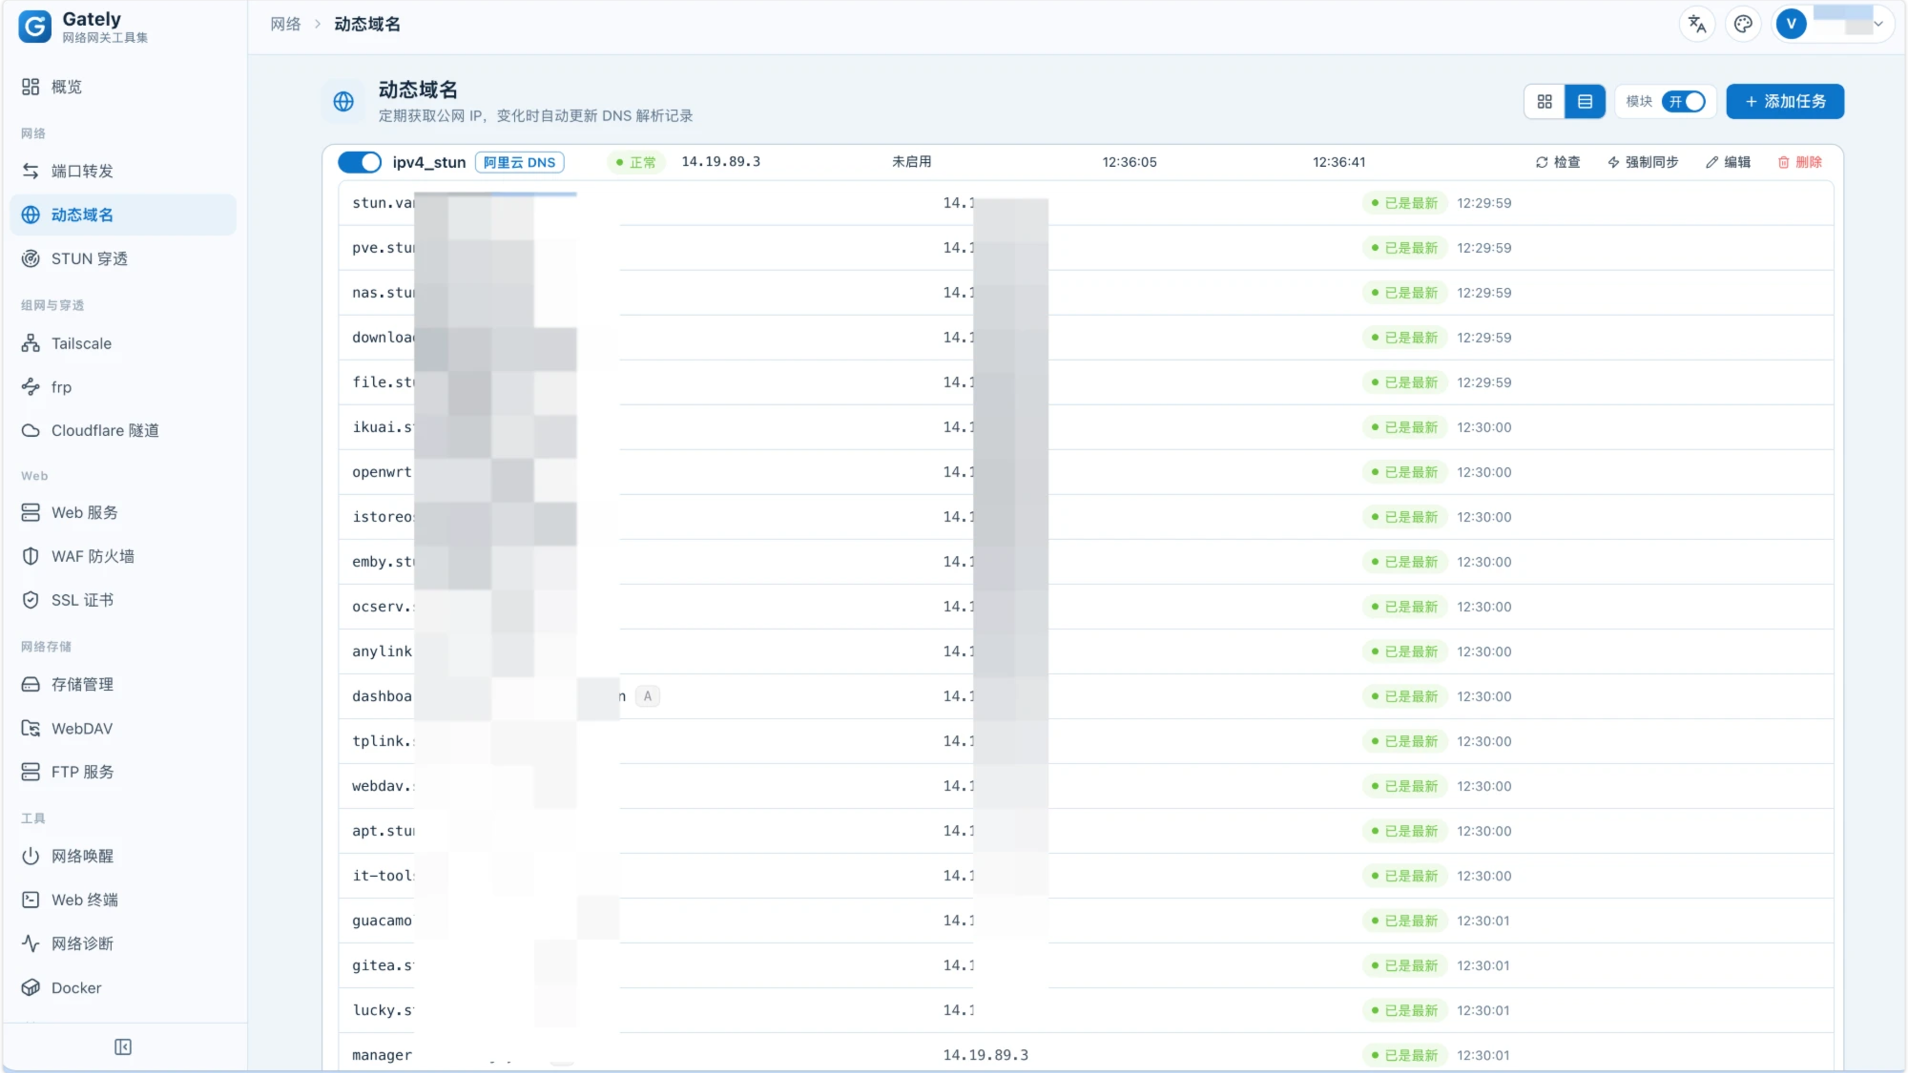
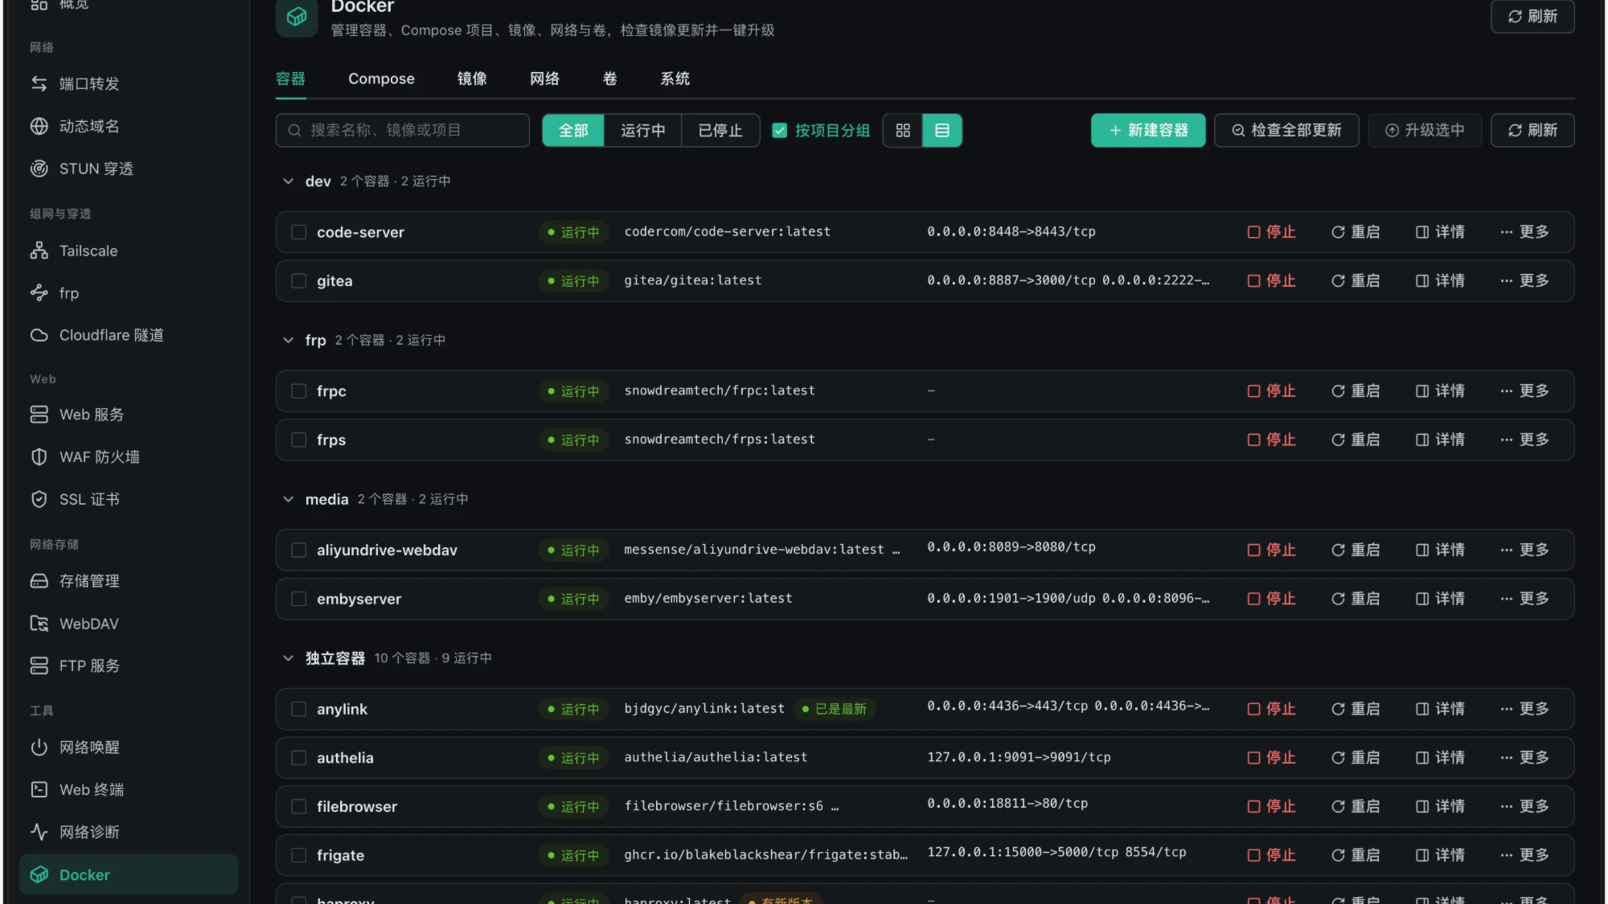
Gately 是一个开源、可审计的网络网关工具集:DDNS(阿里云、Cloudflare、腾讯云、DNSPod、 华为云等)、STUN 穿透、端口转发(多目标故障转移、流量统计)、SSL 证书(ACME DNS-01 自动签发)、反向代理与 Web 服务(认证、IP 黑白名单、限流、缓存)、WAF(Coraza + OWASP CRS v4)、Web 终端(SSH/Telnet/SFTP)、网络诊断、通知中心、计划任务等, 单文件约 22 MB,支持导入 Lucky 配置。 懒猫微服包采用 host 网络模式以支持端口转发与 STUN 穿透;因微服容器环境限制, Docker 管理模块不可用,其余功能完整。
懒猫评分/评论
0.0
0 条评论
应用信息
新功能
版本历史记录
New / 新功能 • Protocol Routing: a new module that identifies the protocol from the first bytes of each connection, so HTTPS, SSH, RDP, OpenVPN and 20 protocols in total share one port without decryption. TLS is routed by SNI and ALPN, HTTP by Host, Minecraft by server address; SSH, RDP, SOCKS4/5, OpenVPN over TCP, XMPP, MQTT, PostgreSQL, RTSP, SIP, Redis, AMQP, SMB, Git, IRC, ADB and BitTorrent get one route each; a wait-timeout route serves server-first protocols such as VNC, and the detection timeout accepts tenths of a second. Per-route PROXY protocol and hit counters. / 协议分流:新模块,按连接的首个数据包识别协议,让 HTTPS、SSH、RDP、OpenVPN 等 20 种协议共用一个端口且不解密。TLS 按 SNI 与 ALPN、HTTP 按 Host、Minecraft 按服务器地址分流;SSH、RDP、SOCKS4/5、OpenVPN(TCP)、XMPP、MQTT、PostgreSQL、RTSP、SIP、Redis、AMQP、SMB、Git、IRC、ADB、BitTorrent 各一条路由;「等待超时」路由接收 VNC 等服务端先发言的协议,识别超时可精确到 0.1 秒。每条路由可单独发送 PROXY 协议并显示命中次数。 • Group and sort every list (#48): search, drag-and-drop sorting, bulk moves to a group, group renaming and merging across Dynamic DNS, port forwarding, protocol routing, sites, STUN, certificates, WAF, intrusion prevention, frp, tunnels, File Browser, mounts, Wake-on-LAN, cron, notifications, terminal connections and API tokens; DNS records inside a task can be grouped too. Regrouping never restarts a running instance. / 所有列表支持分组与排序(#48):动态域名、端口转发、协议分流、站点、STUN、证书、WAF、入侵防护、frp、隧道、File Browser、存储挂载、网络唤醒、计划任务、通知、终端连接与 API 令牌统一支持搜索、拖动排序、批量移动到分组、重命名与合并分组;任务内的解析记录也可分组。调整分组不重启运行中的实例。 • STUN addresses in Dynamic DNS (#47): record values and Webhooks can use {STUN_rule_PORT}, {STUN_rule_IP}, {STUN_rule_ADDR} (by rule name or key); tasks sync as soon as the STUN address changes, and a Webhook-only reference still fires. / 动态域名引用 STUN 地址(#47):记录值与 Webhook 可用 {STUN_规则名_PORT} 等变量(规则名或 key),STUN 地址变化后立即同步,只在 Webhook 中引用也会调用。 • STUN behind multiple NATs: with UPnP / NAT-PMP, the gateway's own external address is checked first; behind an outer NAT only the tunnel mapping is kept, so the public port stops drifting. / STUN 适配多层 NAT:开启 UPnP / NAT-PMP 时先查询网关外网地址,外层还有 NAT 时只保留通道端口映射,公网端口不再漂移。 • Delete a single record from a DDNS task card; single-row mobile terminal key bar that follows the on-screen keyboard; opaque home screen icons and a web app manifest; redesigned website home page and README. / DDNS 任务卡片可直接删除单条记录;手机 Web 终端按键栏改为单行并随软键盘显示;修复主屏幕图标透明并提供 Web App Manifest;官网首页与 README 改版。 Security / 安全加固 • While the default password is in use, security settings are read-only, including backup restore and rolling them back from history. / 仍在使用默认密码时安全配置只读,从备份恢复与回滚历史版本同样被拒绝。 • Read-only accounts and tokens get masked credentials, including URL passwords, query values, token-like path segments and URLs inside log text. / 只读账号与令牌读到的凭据一律打码,包括地址中的密码、查询参数、像令牌的路径段以及日志文本中的地址。 • Browsing files/ and sftp/ needs write access; password-only logins no longer reset the failure counter; stricter X-Forwarded-For / X-Real-IP handling; command-capable token scopes are marked "Runs commands"; UPnP control URLs must belong to the replying device. / 浏览 files/、sftp/ 需要写权限;只靠密码的登录不再清零失败计数;X-Forwarded-For 与 X-Real-IP 处理更严格;可执行命令的令牌权限会标注提醒;UPnP 控制地址必须属于应答设备。 Fixes / 修复 • Editing an intrusion prevention rule that has matched before failed with unknown field "lastSeen". / 入侵防护规则命中过后再编辑保存报 unknown field "lastSeen"。 • With several certificates for one domain, the one expiring last is used; list order and groups no longer change the served certificate. / 多张证书覆盖同一域名时使用到期最晚的一张,列表排序与分组不再影响实际使用的证书。 • Protocol Routing no longer forwards zero padding when a ClientHello times out half-way, and stopping a rule closes connections still being identified. / 协议分流在 ClientHello 中途超时时不再转发补零数据,停止规则时立即关闭识别中的连接。 • STUN variables in a JSON Webhook body were not replaced. / JSON 格式的 Webhook 正文中 STUN 变量未被替换。 Upgrading / 升级 • On first start, SNI routing rules in Port Forwarding move to Protocol Routing with their keys, names, groups and routes; the module stays off if Port Forwarding was off, and tokens with portforward access also get protoroute access. Use /api/protoroute/rules (routes instead of sniRoutes); /api/portforward/rules rejects mode. Metrics are now gately_protoroute_*. / 首次启动时端口转发中的 SNI 分流规则自动移到协议分流,key、名称、分组与路由保持不变;端口转发关闭的协议分流也关闭;有 portforward 权限的令牌同时获得 protoroute 权限。接口改用 /api/protoroute/rules(sniRoutes 改为 routes),/api/portforward/rules 不再接受 mode,指标改为 gately_protoroute_*。 • Docker: pull the new image and recreate the container. OpenWrt: install the new .apk / .ipk. fnOS: install the new .fpk in the App Center. Other installs can upgrade online in Settings. / Docker 拉取新镜像后重建容器;OpenWrt 覆盖安装新的 .apk / .ipk;飞牛在应用中心安装新版 .fpk;其他部署方式可在「系统设置」中在线升级。 Release notes: https://gately.cn/en/news/v0.6.2 · 更新说明:https://gately.cn/news/v0.6.2
此 App 尚未收到足够的评分或评论,无法显示评论列表。